
Ranked by severity
The most dangerous issues sit at the top, so limited time goes where it matters first.
Across every engine
A list of vulnerabilities helps no one on its own. AutoST pulls every finding into a single plan, ranks it by severity and tells your engineers exactly what to change.
In short
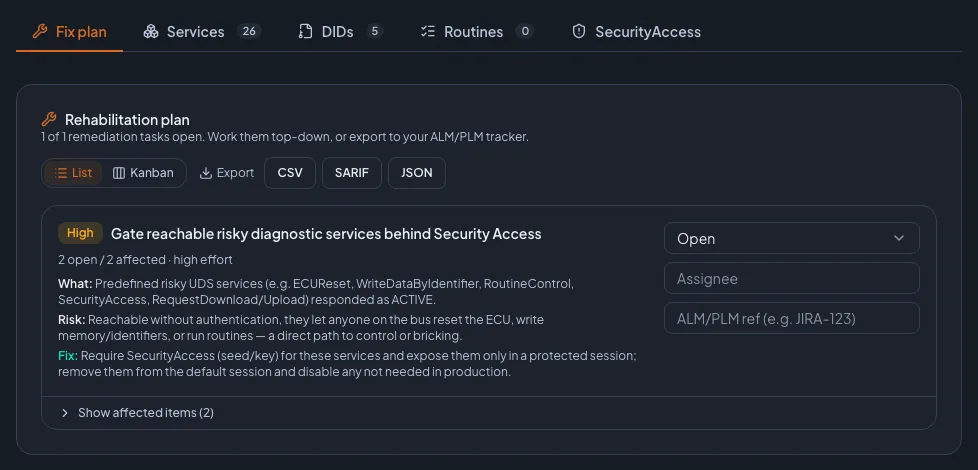
The Fix Plan is a shared remediation view across all AutoST engines (UDS enumeration, SecurityAccess, DoIP, SOME/IP and Android IVI). Each finding becomes one workable task, ranked by severity, with a plain description of what was found, why it matters and how to fix it. Tasks have a workflow state (open, in progress, done), assignees and an ALM/PLM reference field, can be viewed as a list or a Kanban board, and export to CSV, SARIF 2.1.0 and JSON.
What makes it workable
The most dangerous issues sit at the top, so limited time goes where it matters first.
Every task explains the finding, its impact and a concrete remediation, in language a developer can act on.
Workflow state, assignees and an ALM/PLM reference, in a list or a Kanban board, so nothing is lost.
Export
The fix plan exports as SARIF 2.1.0, so it drops straight into code-scanning dashboards and the tools your developers already watch. CSV and JSON are there for everything else.
Because findings and their risk acceptance carry over between scans, a re-test shows what got fixed and what is still open, without re-triaging the whole list.
FAQ
Yes. Findings from UDS enumeration, SecurityAccess, DoIP, SOME/IP and Android IVI all land in one shared plan.
Export as SARIF 2.1.0, CSV or JSON. SARIF fits code-scanning dashboards directly; each task also has an ALM/PLM reference field.
See it on your ECU
Book a one-hour live demo. We scan a real target, walk through the findings and the Fix Plan, and answer whatever you throw at us.

Your demo is withTom ZaubermannFounder of Zyberum, ex-lead of the VW InCar Security Testing Lab
Already trusted by Tier 1, Tier 2 suppliers and OEMs. References on request.
We reply within one business day.
Your privacy
We use cookies and similar technologies to measure our website and the success of our ads. You decide which ones we may use. You can change your choice at any time via "Cookie settings" in the footer. Privacy policy