
Seed randomness
Flags constant, zero, low-entropy or incrementing seeds, measured over multiple requests.
Engine · SecurityAccess
SecurityAccess (0x27) is what stands between an attacker and the dangerous services. AutoST checks whether that gate is real: random seeds, a strong key algorithm, a working lockout and an enforced sequence.
In short
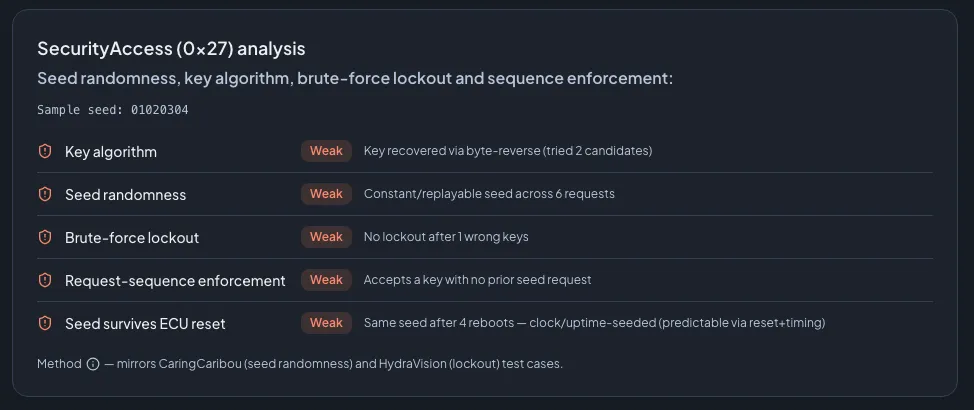
The SecurityAccess engine actively tests UDS service 0x27. It measures seed randomness (constant, zero, low-entropy or incrementing seeds), attempts to recover the seed-to-key algorithm and tries a catalogue of default keys, checks whether a brute-force lockout triggers after wrong keys, and verifies that the ECU enforces the request-seed-then-send-key sequence. An opt-in ECU-reset probe checks whether the seed is predictable across reboots. Every probe is bounded and non-destructive by default; the reset probe is gated behind a confirmation.
What it checks
Flags constant, zero, low-entropy or incrementing seeds, measured over multiple requests.
Attempts to recover a weak seed-to-key relationship and tries a catalogue of known default keys.
Checks whether the ECU locks out after repeated wrong keys, or lets an attacker keep trying.
Verifies the ECU rejects a key that was sent without first requesting a seed.
Opt-in: checks whether the same seed returns after an ECU reset, a sign of clock- or uptime-seeded generation.
The test cases mirror established research (CaringCaribou for seed randomness, HydraVision for lockout).
FAQ
The core probes are bounded and non-destructive. The one exception is the optional ECU-reset predictability probe, which resets the ECU and is therefore gated behind an explicit confirmation.
If AutoST can derive the key from the seed with a simple transformation, or a default key from a known catalogue unlocks the ECU, the seed/key scheme is reported as weak.
See it on your ECU
In one hour we scope a pilot: your bench, your protocols, the targets and what success looks like.

Your demo is withTom ZaubermannFounder of Zyberum, ex-lead of the VW InCar Security Testing Lab
Already trusted by Tier 1, Tier 2 suppliers and OEMs. References on request.
We reply within one business day.
Your privacy
We use cookies and similar technologies to measure our website and the success of our ads. You decide which ones we may use. You can change your choice at any time via "Cookie settings" in the footer. Privacy policy