UDS enumeration
Discovers diagnostic endpoints, sessions, every service and the readable DIDs, and flags the risky ones.
UDS enumerationAutomotive ECU security testing
AutoST connects to an ECU on your bench, maps its diagnostic surface, fuzzes it, checks its SecurityAccess and hands your team a ranked fix plan. The depth of a specialist, run by your own test engineers.
In short
AutoST is an automated security testing platform for automotive ECUs, made by Zyberum GmbH in Germany. A test agent (Carbyne) connects to an ECU on the bench over CAN, CAN FD, DoIP or SOME/IP, while a web dashboard orchestrates the scans. It enumerates diagnostic sessions, services and data identifiers, imports ODX and CDD files to name DIDs and run routines, probes UDS SecurityAccess (0x27), fuzzes UDS and CAN, checks Android infotainment units over ADB, scores the risk and produces a ranked fix plan with PDF, SARIF, CSV and JSON output. It runs on your own servers or hosted by Zyberum and fits into CI/CD pipelines.
How it works
No security specialists required. A test engineer wires it up and AutoST does the rest.
Define the ECU in the dashboard and pair the Carbyne agent on your bench. It talks CAN, CAN FD, DoIP and SOME/IP through a SocketCAN, Vector or Panda interface.
Pick the engines: enumeration, fuzzing, SecurityAccess, DoIP/SOME/IP, IVI. Upload an ODX or CDD file to name DIDs and drive routines. Watch progress live.
AutoST ranks every finding by risk, groups it into a fix plan with concrete remediation, and exports PDF evidence plus SARIF, CSV or JSON for your tracker.
The dashboard
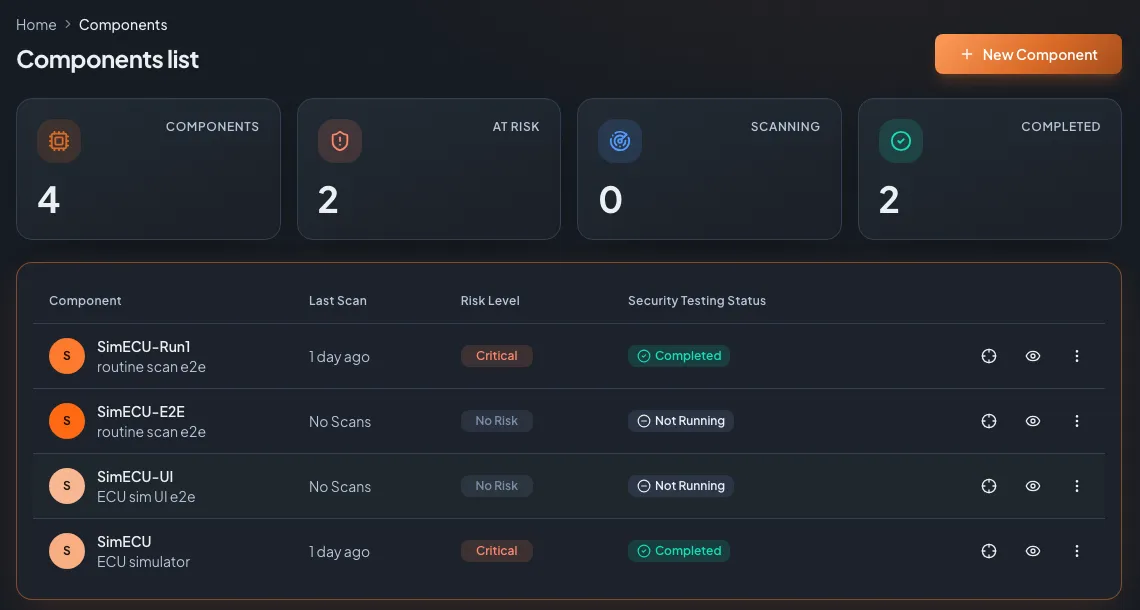
Components grouped by project or vehicle line, each with a risk badge and the status of its last scan. Roles and groups keep teams and suppliers apart.
The engines
Each engine is a focused security test. Run one, or run them all and let the fix plan pull the findings together.
Discovers diagnostic endpoints, sessions, every service and the readable DIDs, and flags the risky ones.
UDS enumerationImports ODX, PDX and CDD to name DIDs and call the right routines (0x31), with opt-in write-probing.
DID & routinesTests seed randomness, weak seed/key algorithms, default keys, brute-force lockout and sequence enforcement.
SecurityAccessReproducible UDS and CAN fuzzing with live crash detection via TesterPresent and DTC monitoring.
ECU fuzzingUDS over IP, DoIP routing activation and vehicle discovery, plus SOME/IP service and method mapping.
DoIP & SOME/IPRecon and hardening checks for Android infotainment over ADB: permissions, exposed components, SELinux.
IVI testingThe fix plan
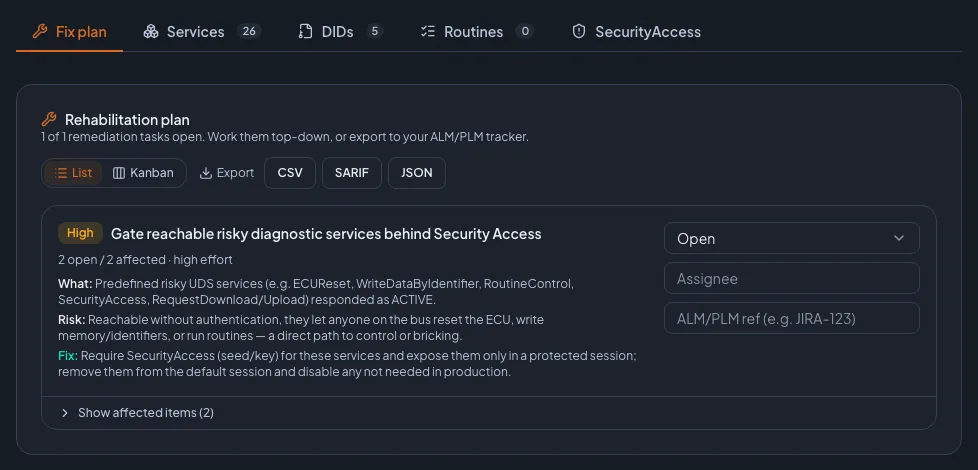
Every finding across every engine lands in one rehabilitation plan, ranked by severity. Each task says what was found, why it matters and how to fix it, with a workflow state and export to your ALM or PLM tracker.
Why teams pick AutoST
Your QA and test engineers run deep security tests. The hard-won knowledge is baked into the engines.
Reproducible seeds, API tokens and a CI plugin mean the same scan runs on every build, not once a year.
Run AutoST on your own servers or let us host it. Test results and reports belong to you.
The alternative
| AutoST | Manual pentest | Home-grown scripts | |
|---|---|---|---|
| Coverage of UDS, DoIP, SOME/IP, IVI | One platform, all of them | Depends on the tester | Whatever you had time to script |
| Repeatable on every build | Yes, via API and CI plugin | No, a point-in-time engagement | Only if you maintain them |
| Ranked fix plan with evidence | Built in, exportable | In the final report | You write it yourself |
| Runs without security specialists | Yes | No | Needs the author |
A pentest and AutoST work well together: use AutoST for broad, repeatable coverage and bring in specialists for the deep, creative work.
FAQ
AutoST tests automotive ECUs: it enumerates UDS diagnostics (sessions, services, DIDs), scans routines from ODX/CDD files, probes SecurityAccess (0x27), fuzzes UDS and CAN, tests DoIP and SOME/IP, and checks Android infotainment units over ADB. It scores the risk and produces a ranked fix plan.
No. AutoST is built so QA and test engineers can run deep security tests. You wire the ECU to the bench agent, pick the engines and read the results. The security knowledge is in the engines.
CAN and CAN FD (ISO-TP), UDS (ISO 14229), XCP and CCP, DoIP (ISO 13400) and SOME/IP. The Carbyne bench agent runs on Windows and Linux and works with SocketCAN, Vector XL and comma.ai Panda interfaces.
Yes. AutoST runs on your own servers as a container, or hosted by Zyberum. Test data and reports stay with you. It is multi-tenant with role-based access and groups.
Yes. AutoST has long-lived API tokens and a CI plugin that triggers a scan, polls for the result, fails the build on findings and emits JSON, JUnit XML and a PDF. Any CI system can drive it through the REST API.
AutoST is built by Zyberum GmbH, an automotive security team in Hannover, Germany, founded by Tom Zaubermann, former lead of the InCar Security Testing Lab at Volkswagen AG.
See it on your ECU
Book a one-hour live demo. We scan a real target, walk through the findings and the Fix Plan, and answer whatever you throw at us.
Your demo is withTom ZaubermannFounder of Zyberum, ex-lead of the VW InCar Security Testing Lab
Already trusted by Tier 1, Tier 2 suppliers and OEMs. References on request.
We reply within one business day.
Your privacy
We use cookies and similar technologies to measure our website and the success of our ads. You decide which ones we may use. You can change your choice at any time via "Cookie settings" in the footer. Privacy policy