
Permissions & components
Dangerous permissions granted to shell, exposed activities and services, and the SELinux posture of the device.
Engine · Infotainment
Modern infotainment runs Android, with apps, permissions and services like any device. AutoST connects over ADB and runs a full hardening assessment of the head unit.
In short
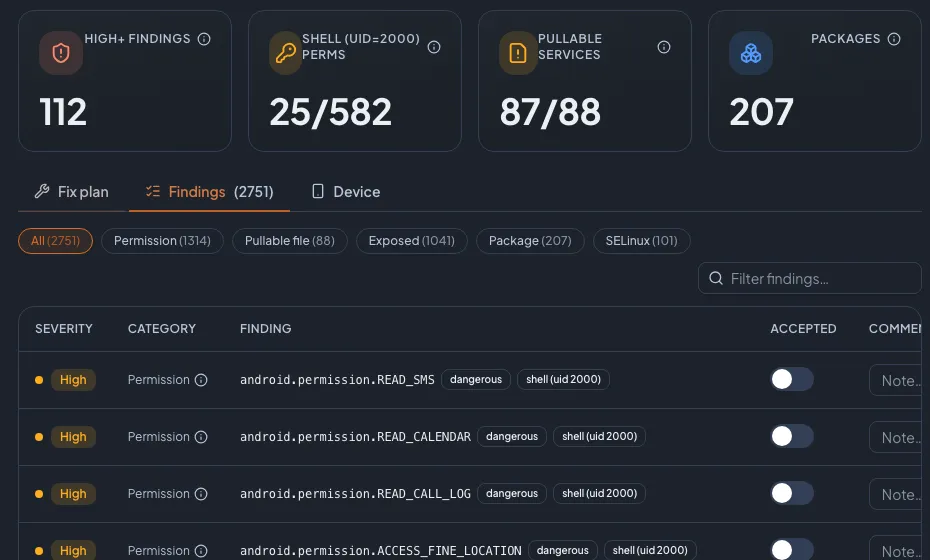
The IVI engine assesses Android infotainment units over ADB. It performs recon of packages, permissions, exposed components, pullable files and SELinux posture, runs static analysis of APKs (manifest flags and secret scanning), and can run functional tests with screenshots and live logcat streaming. Findings are grouped by severity with per-finding remediation and flow into the shared fix plan.
What it assesses
Dangerous permissions granted to shell, exposed activities and services, and the SELinux posture of the device.
System and app files that can be pulled off the device, a common path to secrets and sensitive data.
Manifest flags and secret scanning across installed APKs, to catch debuggable builds and hard-coded credentials.
Functional tests with screenshots and live logcat streaming, so you see the device as it runs.
FAQ
Over ADB, the Android Debug Bridge, to a head unit or an emulator. From there it enumerates packages, permissions, components and files.
No. Each finding comes with remediation, and all of them flow into the shared fix plan alongside the UDS, DoIP and SOME/IP findings.
See it on your ECU
In one hour we scope a pilot: your bench, your protocols, the targets and what success looks like.

Your demo is withTom ZaubermannFounder of Zyberum, ex-lead of the VW InCar Security Testing Lab
Already trusted by Tier 1, Tier 2 suppliers and OEMs. References on request.
We reply within one business day.
Your privacy
We use cookies and similar technologies to measure our website and the success of our ads. You decide which ones we may use. You can change your choice at any time via "Cookie settings" in the footer. Privacy policy