
About
We build the tool we always wanted.
AutoST comes from a team that has spent years taking ECUs apart by hand. We automated what we learned, so your engineers get the same depth without the same decade of practice.
In short
AutoST is built by Zyberum GmbH, an automotive and embedded security team in Hannover, Germany, founded in 2019 by Tom Zaubermann, who previously led the InCar Security Testing Lab at Volkswagen AG. The team does hands-on ECU penetration testing and automated what it learned into AutoST. Its certifications include OSCP and the SAE and TÜV SÜD Automotive Cybersecurity certification for ISO/SAE 21434.
The maker
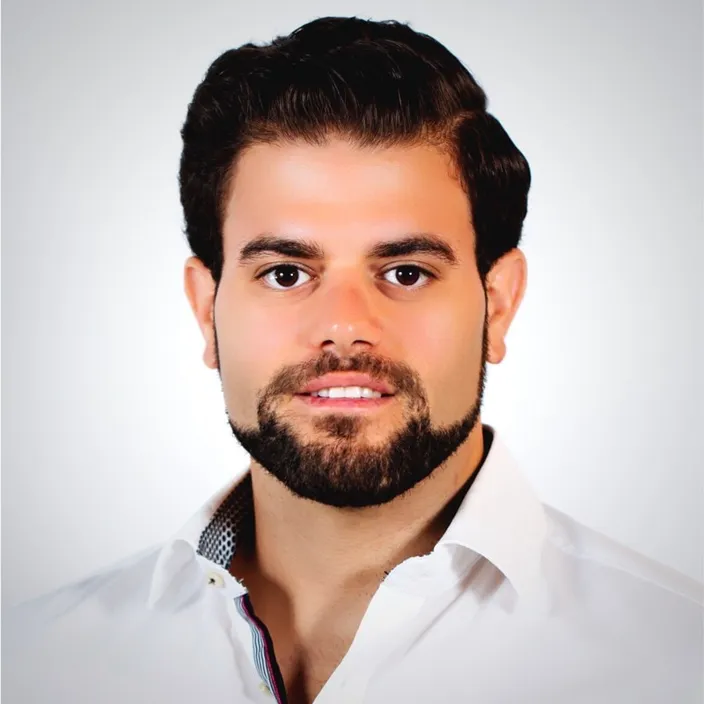
The person behind AutoST
Tom Zaubermann founded Zyberum in 2019. Before that he led the InCar Security Testing Lab at Volkswagen AG, where his work was pentesting ECUs and building security into how they are developed.
AutoST grew out of that work: the checks a good tester does by hand on a bench, turned into engines that anyone on the team can run. He speaks about car hacking and API security at conferences such as code.talks and on podcasts.
- Founder of Zyberum since 2019
- Former lead of the InCar Security Testing Lab at Volkswagen AG
- OSCP and ISO/SAE 21434 (SAE / TÜV SÜD) certified
- Speaks English and German
Credentials
Certified where it counts
Certificates do not find vulnerabilities, people do. These are the ones our customers ask for.
OSCP
Offensive Security Certified Professional
OffSec
Automotive Cybersecurity Level 1 & 2
Automotive Cybersecurity Certification for ISO/SAE 21434
SAE International · TÜV SÜD
ISO/IEC 27001 Auditor
Information security management systems
CRA Auditor
EU Cyber Resilience Act
CCISO
Certified Chief Information Security Officer
Technion
On stage and on air
Talks and podcasts
A selection of Tom talking about car hacking and application security.
Pressing play loads the video from YouTube.
The company
A product from a working security team
Zyberum is a cybersecurity company from Hannover. AutoST is its automotive product, built and used by the same people who do ECU penetration testing day to day.
That is the point of difference: AutoST is not a spec someone wrote, it is the distilled practice of a team that breaks ECUs for a living, and keeps feeding what it finds back into the tool.
See it on your ECU
See AutoST run against your kind of ECU
Book a one-hour live demo. We scan a real target, walk through the findings and the Fix Plan, and answer whatever you throw at us.
- A security engineer runs it, not a sales rep
- Bring your own protocol and hardware questions
- Free, and a clear next step afterwards

Your demo is withTom ZaubermannFounder of Zyberum, ex-lead of the VW InCar Security Testing Lab
Already trusted by Tier 1, Tier 2 suppliers and OEMs. References on request.
Or send us a message
We reply within one business day.